Security News 2026-10-11

Archived week: Sun, Oct 11 – Sat, Oct 17, 2026 · 330 stories

Saturday, October 17

Cyber Security News
OpenCode Security Breach Exposes Third-Party API Keys of its Console Users
Cyber Security News11:20 PM

OpenCode has disclosed a security breach affecting 1.4% of its Console users, warning that third-party API keys saved in affected workspaces may have been exposed. In an October 17 statement, the company linked the incident to a large-scale distillation attack and said it was working with Anthropic, OpenAI, and Google to address it. The affected […] The post OpenCode Security Breach Exposes…

r/netsec
PhantomBuffer: Effective EDR Evasion Through Stealth Injection
r/netsec9:30 PM

PhantomBuffer EDR evasion uses stealth injection via SendMessage with WM_SETTEXT to effective bypass EDR (Endpoint Detection and Response). Unlike traditional edr bypass techniques, it does not use the VirtualAllocEx and WriteProcessMemory APIs .

Cyber Security News
Claude AI Solves 25-Year NSA Cryptography Mystery in Just 30 Minutes
Cyber Security News11:59 AM

Anthropic says an internal Claude research model has traced the origins of five NSA-supplied elliptic curve seeds in under 30 minutes, answering a cryptography question that remained open for roughly 25 years. The finding explains how important public security parameters were chosen, rather than exposing secret keys or breaking encryption. In a report published October […] The post Claude AI…

The Hacker News
MALFEX npm Package 'imgdecode' Hides Shellcode Loader in Windows Native Addon
The Hacker News6:11 AM

Cybersecurity researchers have discovered a malicious npm package that's part of a recently disclosed software supply chain attack campaign dubbed MALFEX. The package, named "imgdecode," was uploaded to the package registry on September 30, 2026, by a user named "malfexteste8." It has been downloaded 979 times as of writing and is still available on npm as of writing. The latest version of

Cyber Security News
Hackers used Compromised ConnectWise Backup Credentials to Hack 173 Microsoft 365 Accounts
Cyber Security News5:52 AM

Hackers used a stolen ConnectWise Cloud Backup credential to sign in to 173 Microsoft 365 partner and customer tenants, giving them access through a trusted backup application. The incident shows how one leaked vendor secret can create risk across many organizations when a multitenant app already has wide permissions. The affected product is ConnectWise Cloud […] The post Hackers used Compromised…

The Hacker News
Hackers Use Compromised ConnectWise Credential to Sign In to 173 Microsoft 365 Tenants
The Hacker News1:16 AM

Cybersecurity researchers are sounding the alarm related to an active campaign in which unknown threat actors are abusing a compromised Microsoft 365 (M365) credential belonging to ConnectWise Cloud Backup (formerly SkyKick) to gain unauthorized access to customers' M365 environments. ConnectWise Cloud Backup is a cloud-based backup and recovery service built for managed service providers (MSPs

Cyber Security News
Google Fixes 10 Chrome Vulnerabilities, Including Memory Corruption Flaw Found With Claude AI
Cyber Security News12:29 AM

Google released a Chrome Stable security update fixing 10 vulnerabilities across Windows, Mac, and Linux, including a high-severity DOM memory corruption flaw reported by Xinyang Ge of Anthropic with Claude AI. The update also addresses one critical, six high-severity, and three medium-severity vulnerabilities. Google announced the update on October 15, 2026. Google is rolling out […] The post…

Cyber Security News
Hackers Exploit Critical Collabora Online Flaw to Backdoor Nextcloud Servers
Cyber Security News12:24 AM

Hackers are exploiting a critical flaw in the Collabora Online Built-in CODE Server app for Nextcloud, with users reporting web shells on compromised servers. Tracked as CVE-2026-110447, the vulnerability allows remote attackers to run operating system commands without logging in. It affects the richdocumentscode app before version 26.4.303 and carries a CVSS v4 score of […] The post Hackers…

Friday, October 16

Cyber Security News
OpenAI Confirms Its AI Model Hacked Government Website While Counting Hospital Beds
Cyber Security News11:15 PM

OpenAI has confirmed that an internal AI model hacked an unnamed government statistics website while trying to count hospital beds. The June 17, 2026 incident started as a data task during reinforcement-learning training, but turned into unauthorized access involving server files, exposed credentials, fake login tokens, and 24 years of downloaded statistics. OpenAI found the […] The post OpenAI…

Schneier on Security
Friday Squid Blogging: Squid Before the Chicxulub Meteor Impact
Schneier on Security4:06 PM

New research shows that squid lived all around the globe even before the Cretaceous-Paleogene mass extinction event. As usual, you can also use this squid post to talk about the security stories in the news that I haven’t covered. Blog moderation policy.

BleepingComputer
Critical BlockStrap flaw lets hackers run code on Magento servers
BleepingComputer3:00 PM

Researchers warn that hackers could soon exploit a maximum-severity vulnerability (CVE-2026-103849) affecting Magento and Adobe Commerce, potentially allowing them to execute arbitrary PHP code on store servers. [...]

The Hacker News
Researchers Demonstrate OpenBSD Root Exploit Chaining 37-Year-Old Shared-Memory Bug
The Hacker News12:48 PM

A local privilege escalation exploit published today gains root on OpenBSD 7.9 by chaining a roughly 37-year-old integer overflow with a separate kernel flaw, bypassing OpenBSD's KARL kernel-address randomization and its SMAP and SMEP hardware protections. Security firm Calif, which found and reported the flaws, published a detailed writeup and full proof-of-concept code after OpenBSD shipped

The Hacker News
Attackers Tampered with AOMEI Backupper's Update Servers for Minutes to Deliver a Backdoor
The Hacker News11:43 AM

Attackers repeatedly changed the files that AOMEI Backupper fetches from the vendor's own update servers, in windows of five to ten minutes at a time between May and July 2026, so that any copy of the Windows backup program that checked for an update during one of those windows would download and run a backdoor. Google Threat Intelligence Group, Mandiant, and ManageEngine's Threat Analysis

The Hacker News
UAT-11985 Uses Fake Event Invites to Target Taiwan Research Affiliates With Google AitM Phishing
The Hacker News11:16 AM

Cybersecurity researchers have disclosed details of an advanced persistent threat (APT) spear-phishing campaign that has targeted individuals affiliated with Taiwan research organizations to direct victims to an adversary-in-the-middle (AitM) phishing framework designed to harvest their Google account credentials and multi-factor authentication (MFA) codes. The activity is being tracked by

Cyber Security News
Hackers Use New ROMULUS ClickFix Platform to Deliver Malware and Evade Security Detection
Cyber Security News9:42 AM

Hackers are using a newly identified platform called ROMULUS to deliver malware through ClickFix traps, combining hidden PowerShell scripts, altered software installers, and encrypted archives. The platform supports separate infection paths, including one that installs LegionLoader and another that abuses a legitimate Stardock program to load malicious code. The findings show how a single…

r/netsec
16% of RPKI-covered IPv4 routes still allow a forged-origin hijack that passes validation, the setup behind the Virtualizor update attack
r/netsec9:40 AM

Author here, I work at IPinfo. some security-relevant highlights part of the post: The August 28 Virtualizor update attack used a forged-origin /24 inside Hetzner’s space. From what we saw, it was RPKI-valid because Hetzner’s ROA covered the /16 and allowed announcements down to /24, and no real /24 existed to compete with it. We also measured how common that setup is. In this case, of 855,217…

r/netsec
CVE-2026-108082: Symfony ReDoS. One request. Seconds of CPU
r/netsec9:32 AM

If you run Laravel (or anything on Symfony), read this. CVE-2026-108082: one unauthenticated GET, seconds of backend CPU, ~100 requests and the app times out. A dumb ReDoS that common config turns into a real DoS. 👀⤵️

Cyber Security News
New YuanKong Android RAT Hijacks Phones to Steal Banking PINs and Passwords
Cyber Security News9:08 AM

A newly analyzed Android remote-access Trojan called YuanKong can watch and control a victim’s phone, capture passwords and payment PINs, and send stolen information to operators. Rather than relying on access to text messages or contact lists, it uses Android’s Accessibility features and screen controls to observe what people do inside apps, including banking and […] The post New YuanKong…

The Hacker News
OpenAI Research Model Spent 3rd-Party Test ETH Without Permission to Deploy Smart Contract
The Hacker News9:03 AM

OpenAI has disclosed seven new incidents in which its artificial intelligence (AI) models exhibited misaligned behavior, including one case where its research model, after not having funds on an Ethereum test network, spent test cryptocurrency from a third-party's wallet without authorization to complete a coding task. The incident, the AI company said, involved an internal research model part

Cyber Security News
37-Year-Old Kernel Flaw Exploited to Gain Root Access on OpenBSD — PoC Released
Cyber Security News9:01 AM

A proof-of-concept exploit that gains root access on OpenBSD by chaining two kernel flaws. The main bug dates back about 37 years to the original BSD source code. According to Security researchers at Calif, the flaw survived because a shared memory attachment counter named shm_nattch used a signed 16-bit value. OpenBSD fixed both issues before […] The post 37-Year-Old Kernel Flaw Exploited to…

BleepingComputer
Employees using personal ChatGPT at work? Here's what IT admins need to do
BleepingComputer8:50 AM

Employees using personal ChatGPT accounts at work can expose sensitive company data, even when their organization provides an approved Enterprise workspace. NordLayer explains how IT teams can investigate unauthorized AI use and block sensitive information before it reaches personal accounts. [...]

Cyber Security News
Hackers Use AI-Generated Scripts to Hijack Linux Sudo Commands and Steal Passwords
Cyber Security News8:23 AM

A campaign against government organizations and state-linked infrastructure used AI-assisted scripts to steal credentials, maintain access to Linux servers and seek sensitive data, according to new research. The attackers altered users’ shell startup files to intercept the sudo command, then copied entered passwords to a file while passing them to the real command. This let […] The post Hackers…

Cyber Security News
Hackers Abuse 20,000 Cloudflare Pages Domains to Push Fake Microsoft Security Alerts
Cyber Security News7:43 AM

Hackers have abused more than 20,000 Cloudflare Pages domains over six months to spread fake Microsoft security alerts and steer users toward scam call centers. The campaign uses Help Traffic Distribution System, or Help TDS, to route visitors from compromised websites, malicious ads, social media, and spam into tech support scams. The pages claim that […] The post Hackers Abuse 20,000 Cloudflare…

Cyber Security News
Hackers Use Codex and DeepSeek AI Agents to Breach 440 PaperCut Servers Worldwide
Cyber Security News7:23 AM

A cybercrime campaign used hundreds of AI agents to target internet-facing PaperCut NG and MF print-management servers, compromising at least 440 instances linked to 395 organizations in 48 countries, according to GreyNoise. The operation paired OpenAI’s Codex coding-agent harness with a DeepSeek model and common security tools, allowing the operator to develop and test exploits […] The post…

Cyber Security News
iOS 27.0.1 Untethered Jailbreak Demonstrated on iPhone 18 Pro
Cyber Security News7:21 AM

Security researchers from the cybersecurity firm Calif demonstrated a working untethered jailbreak for iOS 27.0.1 on Apple’s newest iPhone 18 Pro. The live demo took place at Hexacon 2026, the offensive security conference organized by Synacktiv in Paris on October 16. It is one of the first public signs that Apple’s latest phone and software […] The post iOS 27.0.1 Untethered Jailbreak…

The Hacker News
AI Decision Models and Their Impact on AI SOC Platforms
The Hacker News6:30 AM

In the space of a month, a new category of AI model went from nonexistent to everywhere. TypeSafe AI released Jev on September 15 and called it a System One model, a nod to Kahneman's fast, intuitive thinking. OpenAI announced its own Decisions API at DevDay and opened a public beta on October 6. Cribl published cribl-decision, an open LoRA adapter you can run locally. Others, like Laya, are

Cyber Security News
Chinese Phishing Network Uses 17,000 Domains to Target Japanese Banks and Steal Credentials
Cyber Security News6:26 AM

A large Chinese-language phishing operation has used around 17,000 internet domains to impersonate banks, payment services, retailers and other well-known brands, with Japan as its main target. The operation relies on three related phishing kits—CoGUI, CoAceV and CoFish_Ws—to send deceptive emails and direct victims to fake login or payment pages. The findings come as security […] The post…

Schneier on Security
Backdooring Open-Weight AI Models
Schneier on Security6:04 AM

This is a problem: Any open model whose weights have been edited can carry a backdoor, whether it’s a task-specific fine-tune, a merged adapter or an abliterated build. We have abliterated models in the title because it’s the most popular reason people download modified weights without verifying what’s inside. Abliteration is a cheap fine-tune that takes away a model’s ability to refuse. You find…

Cyber Security News
New Aoki Malware Targets ChatGPT, Claude, Codex and Gemini to Steal Credentials
Cyber Security News5:22 AM

Aoki, also known as Aokigahara, is a data-stealing malware that has added credentials for AI tools to its growing list of targets. Recent versions seek local files and session data linked to ChatGPT, Claude, OpenAI Codex, Cursor, Codeium and Gemini. The change raises the risk for developers who use AI assistants alongside source-code repositories, cloud […] The post New Aoki Malware Targets…

Cyber Security News
Google Automatically Adds Your Phone Number to Every Google Account on Your Android Phone
Cyber Security News5:07 AM

Google automatically verifies phone numbers on Android devices and adds them to every Google account signed in on the Phone. The setting is enabled by default, raising privacy concerns for users who keep personal, work, and secondary accounts separate. Google’s documentation confirms that the behavior covers both existing accounts and accounts added later. The feature, […] The post Google…

Cyber Security News
CERT-In Warns Hackers Using AI Agents to Launch Cyberattacks in Just Hours
Cyber Security News4:06 AM

India’s cyber response agency, CERT-In, has warned that hackers are using AI agents to cut the time between gaining access to systems and causing damage from days to just hours. Its critical advisory, issued on October 15, 2026, describes attacks against Indian organizations and separate incidents involving AI agents that exceeded their approved research tasks. […] The post CERT-In Warns Hackers…

Cyber Security News
Hackers Exploit D-Link, Ubiquiti and SAP Flaws to Hijack Devices for Proxy Networks
Cyber Security News4:02 AM

A cybercrime campaign has compromised at least 143 devices in 34 countries by exploiting flaws in D-Link, Ubiquiti and SAP products. The attackers installed Pawns.app proxy software on victim devices, turning their internet connections into residential proxy nodes. That lets the operator route internet traffic through the victims’ real IP addresses, which can make the […] The post Hackers Exploit…

Cyber Security News
MITRE ATT&CK v20 Added 9 New Attack Techniques Covering AI Exploits, MFA Bypass, and CAPTCHA Evasion
Cyber Security News3:58 AM

MITRE released ATT&CK v20 on October 13, adding nine Enterprise techniques that describe how attackers may target AI systems, steal application-specific passwords to bypass multi-factor authentication (MFA), and get around CAPTCHA checks. The update also expands coverage for industrial control systems (ICS) and mobile devices, and adds detection guidance for several of the new behaviors. […] The…

Cyber Security News
Top 10 Best Data Classification Tools in 2026 [Ranked & Scored]
Cyber Security News3:18 AM

Every downstream control DLP, encryption, retention, access inherits its accuracy from classification, which makes this the quiet foundation of data security. We scored the leading options with enforcement wiring weighted highest, and counted honestly: nine distinct vendors from ten sheet rows, since Titus and Boldon James both sell under Fortra. BigID takes 1; Microsoft Purview […] The post Top…

Cyber Security News
BeyondTrust 0-Day Vulnerability Exploited Since August to Gain Full Admin Access in Minutes
Cyber Security News3:17 AM

A critical zero-day vulnerability in BeyondTrust Remote Support was exploited in late August, weeks before the company disclosed the flaw and released a patch. The suspected China-linked espionage group ARMORY CASTLE used the weakness to access appliances, escalate privileges to root, and reach credentials the product stores or handles. Mandiant says the flaw lets an […] The post BeyondTrust…

Cyber Security News
Top 10 Best Tokenization Solutions in 2026 [Ranked & Scored]
Cyber Security News3:06 AM

Tokenization does two very different jobs wearing one name: collapsing PCI audit scope for payment estates, and keeping analytics alive on protected enterprise data. We scored ten solutions across both lanes. Protegrity takes 1 for enterprise-data breadth; Very Good Security and Thales complete the podium. Key Takeaways • 1 overall: Protegrity analytics-preserving tokenization at Fortune-scale…

Cyber Security News
Top 10 Best Encryption & Key Management Solutions in 2026 [Ranked & Scored]
Cyber Security News2:56 AM

Encryption is only as trustworthy as the key custody behind it and with post-quantum migration now a planning requirement, key inventories became strategy documents. We scored ten solutions from native cloud floors to sovereign HSMs. Thales takes 1 for multi-cloud estate control; AWS KMS and Fortanix complete the podium. Key Takeaways • 1 overall: Thales […] The post Top 10 Best Encryption & Key…

The Hacker News
China-Linked Hackers Exploited BeyondTrust Zero-Day to Take Over Remote Support Servers
The Hacker News1:55 AM

The China-nexus cyber espionage group tracked as Armory Castle (previously UNC5221 or Warp Panda) exploited a newly disclosed security flaw in BeyondTrust Remote Support (formerly Bomgar) as a zero-day in late August 2026. The vulnerability, tracked as CVE-2026-102764 (CVSS score: 9.3), is a case of improper origin validation in an internal messaging component that could be exploited by a

The Hacker News
CERT-In Warns AI Agents Accessed Sensitive Data at Indian Organizations During Testing
The Hacker News1:53 AM

AI agents being tested online reached the live systems of Indian organizations and read business records, including personal data and confidential material, CERT-In said in an advisory on October 15. The agents went beyond their assigned tasks, and none of the organizations detected the unauthorized access. After internal reviews, the AI companies whose models were being tested

Cyber Security News
Hackers Target 60 Indian Banking and UPI Apps With New GhostBat Android Malware
Cyber Security News12:33 AM

A new version of GhostBat Android malware is targeting users of 60 banking, UPI, wallet, fintech and payment apps in India. The malware can abuse Android’s Accessibility Service to watch activity in selected apps and capture PIN-like input. Its operators are also using fake mParivahan and eChallan messages to trick people into installing harmful apps. […] The post Hackers Target 60 Indian Banking…

Thursday, October 15

The Hacker News
PEERSTITCH Malware Deployed via FortiOS Flaw Bypasses Checks on Tagged VPN Sessions
The Hacker News11:59 PM

A suspected advanced threat actor has been observed exploiting a security flaw in Fortinet FortiOS to deliver a previously unreported memory-resident ARM64 malware known as PEERSTITCH. The attack involves the exploitation of CVE-2025-61624 (CVSS score: 5.4), a path traversal flaw in the command line interpreter of FortiOS, FortiPAM, FortiProxy, and FortiSwitchManager that could allow a

Cyber Security News
Linus Torvalds Reveals Claude Code Wrote Linux Kernel Patches and Test Programs
Cyber Security News11:07 PM

Linus Torvalds has disclosed that Claude Code helped write Linux kernel patches, test programs, review material, and the first draft of a technical write-up under his direction. The work targets page-cache read performance, showing how AI coding tools are used in core operating-system development while openly documenting technical limits. Torvalds states that Claude Code produced […] The post…

Cyber Security News
Critical Adobe Acrobat Flaw Lets Malicious PDFs Trigger One-Click Memory Corruption
Cyber Security News11:05 PM

Adobe has fixed a flaw in Acrobat and Acrobat Reader that lets a malicious PDF corrupt memory when a user opens it. Tracked as CVE-2026-81983, the out-of-bounds write carries a CVSS score of 7.8 and could lead to code execution with the victim’s user rights. Adobe says it has seen no active exploitation so far. […] The post Critical Adobe Acrobat Flaw Lets Malicious PDFs Trigger One-Click Memory…

Cyber Security News
PoC Exploit Released for Critical GitLab RCE Vulnerability (CVE-2026-97229)
Cyber Security News11:01 PM

A public proof-of-concept (PoC) for CVE-2026-97229 published by researcher Jonah Burgess shows how a flaw in GitLab’s CI/CD regular-expression compiler could be used to run commands on a vulnerable server. GitLab rates the issue Critical with a CVSS score of 10.0. The exploit code is publicly available, raising the risk for organizations that have not […] The post PoC Exploit Released for…

Cyber Security News
Critical Linux Kernel Flaw Lets Attackers Escape Virtual Machines and Take Control of Hosts
Cyber Security News10:06 PM

A critical flaw in the Linux kernel may allow an attacker-controlled virtual machine (VM) to breach its isolation boundary and impact the host system. This vulnerability, identified as CVE-2026-99999 and referred to as PwnEscape by researcher Paulos Yibelo, originates from the Linux networking code rather than a specific hypervisor. Paulos Yibelo demonstrated a technique that […] The post…

The Hacker News
Critical PwnEscape Linux Kernel Vulnerability Lets Guest VMs Read Host Memory
The Hacker News3:24 PM

A newly disclosed critical flaw in the Linux kernel allows code inside a virtual machine to read memory on the host computer it runs on. A researcher demonstrated the leak against Vercel's live cloud sandboxes, and Vercel confirmed it. The flaw, now tracked as CVE-2026-99999 and nicknamed PwnEscape, is in the Linux kernel's networking code, not in any one cloud's setup, so it reaches the shared

The Hacker News
ThreatsDay: Adobe RCE, DNS Wallet Theft, NVIDIA Container Escape, Self-Healing Backdoor + 23 More
The Hacker News1:49 PM

Someone built a tool to steal data, then decided it should scare the victim for fun. Yes, that’s an actual feature. And somehow, it fits right in with this week's security stories. The rest gets interesting in different ways. A small permission can lead to a big theft. A trusted login can hide the wrong person. Old bugs are finding new victims, familiar tools are being put to strange uses, and

Schneier on Security
Measuring Human Cryptanalysis Effort
Schneier on Security11:24 AM

Matthew Green has a new site that tries to estimate the number of cryptanalyst-hours that have been spent analyzing different public-key algorithms: Abstract: We estimate how much public cryptanalysis each public-key assumption has received, using the literature itself as the instrument. From roughly sixteen thousand candidate papers we classify cryptanalytic work on ECDLP, structured and plain…

The Hacker News
Citizen Lab Traces Zero-Click Candiru Spyware Infections at Al Jazeera to Targeted Online Ads
The Hacker News11:01 AM

Candiru, an Israeli maker of spyware sold to governments, infected devices at the news network Al Jazeera through ordinary online ads, in attacks that needed no click or other action from the user, researchers at the Citizen Lab said Thursday. The hidden attack code ran the moment an ad loaded on the screen, and in some cases the ad loaded out of sight, in the background. The Citizen

The Hacker News
Silent Lynx Exploits WinRAR Flaw to Deploy Reverse Shell in CIS Government Attacks
The Hacker News11:00 AM

The threat actor known as Silent Lynx has been attributed to a fresh set of attacks targeting government organizations across the Commonwealth of Independent States (CIS). The activity, observed from June 2025 through August 2026, involves four different infection chains that make use of macro-enabled documents, PS2EXE downloaders, GitHub-hosted PowerShell, and crafted WinRAR archives

Cyber Security News
Burger King Japan Confirms Data Breach Exposing 11.18M User Records
Cyber Security News10:55 AM

Burger King Japan has confirmed a data breach that exposed about 11.18 million records linked to members of its official app. BK Japan, which operates the chain in Japan, said an outside party gained unauthorized access to the system used to manage app member information. The company disclosed the incident on October 15, 2026. According […] The post Burger King Japan Confirms Data Breach Exposing…

Cyber Security News
Critical ChatGPT GitHub Connector Flaw Could Allow Attackers to Steal Private Repository Secrets
Cyber Security News10:47 AM

A critical flaw in ChatGPT’s GitHub integration has the potential to turn a routine repository review into a secret-theft attack. A report published on October 15, 2026, describes a scenario in which manipulated repository instructions allegedly lead an AI agent to modify a different private repository and trigger GitHub Actions. According to the researcher Sunil […] The post Critical ChatGPT…

Cyber Security News
Citrix XenServer Vulnerabilities Could Allow Malicious VM Users to Compromise Host Systems
Cyber Security News9:42 AM

Citrix has disclosed four XenServer vulnerabilities, including three that could let a malicious user with elevated rights inside a virtual machine compromise or crash the underlying host. Citrix published the high-severity bulletin CTX697170 on October 13, 2026, covering XenServer 8.4 and XenServer 9. Citrix lists the advisory in its XenServer security bulletin archive. The host-impacting […] The…

Cyber Security News
Hackers Use ClickFix and Python Tunnels to Prepare Systems for Ransomware Attacks
Cyber Security News9:30 AM

Hackers are using ClickFix tricks to install malware loaders and Python tunnels on Windows systems, creating access that could support ransomware attacks. A late September incident shows how a user running a command can start an infection chain built around trusted Microsoft programs, hidden code, and encrypted network traffic. The attack was stopped before ransomware […] The post Hackers Use…

Cyber Security News
Chinese Phishing Network Linked to 1 Billion Messages Targeting 75,000 Organizations
Cyber Security News9:25 AM

A Chinese-run phishing network has been linked to one billion phishing emails targeting 75,000 organizations, according to a report published on October 14, 2026. The operation centers on Iron Man System, a paid phishing platform that lets criminals deploy fake websites and collect sensitive information without building their own tools. The report lists those headline […] The post Chinese…

Cyber Security News
Just Viewing an Online Ad Can Infect Your Device With Spyware, Researchers Reveal
Cyber Security News9:16 AM

Simply viewing an online advertisement can be enough to infect a device with powerful spyware, without the user clicking, downloading a file, or seeing any warning. Citizen Lab researchers documented what they call the first public technical proof of zero-click mercenary spyware delivered through targeted ads. The method, named “AdFection,” infected devices at international news […] The post Just…

The Hacker News
Help TDS Linked to Hotejka as 20,000+ Cloudflare Pages Domains Host Tech Support Scams
The Hacker News9:11 AM

A long-running Traffic Distribution System (TDS) known as Help TDS to a Russian-language affiliate program called Hotejka, which appears to be a rebrand of a traffic monetization operation dubbed ROI777. Help TDS is assessed to be active since at least 2017, offering PHP code templates to partners and affiliates that are installed into compromised websites with an aim to direct unsuspecting

BleepingComputer
Is AI pentesting as good as a human pentester?
BleepingComputer9:01 AM

AI pentesting can uncover vulnerabilities missed by human testers, but it also has limitations in consistency, risk assessment, and understanding business context. Intruder compares the strengths and weaknesses of both approaches and explains where AI agents can improve security testing. [...]

Cyber Security News
AI Agents Create an Unseen Credential Surface That Exposes API Keys and Cloud Secrets
Cyber Security News8:55 AM

AI agents can expose API keys and cloud secrets during ordinary work, even when no malware is present. When an agent runs a command, reads a configuration file or fetches a secret to complete a task. Even sensitive data can move from protected storage into command histories, logs, agent transcripts and the model’s context. The […] The post AI Agents Create an Unseen Credential Surface That…

The Hacker News
NGINX Fixes 5 Flaws, Including Possible RCE and a TLS Bug That May Skip Client-Cert Checks
The Hacker News7:58 AM

NGINX released versions 1.30.6 and 1.31.7 on October 14 to fix five vulnerabilities, one of them present in every release since May 2005. There are three memory bugs that F5, the company behind NGINX, says could crash a worker process or possibly let an attacker run code, and each requires a specific configuration to exploit. A fourth lets an attacker forge a TLS session that could

Cyber Security News
UK Legal Aid Agency Data Breach Exposes Personal Records Dating Back to 1978
Cyber Security News7:54 AM

The UK Legal Aid Agency (LAA) has confirmed that its 2025 cyberattack stole personal records dating back to 1978. An updated investigation found approximately 250,000 records from before 2007, widening the known scope of a breach that affected legal aid applicants, providers and some probation service users. In its October 14, 2026 update, the agency […] The post UK Legal Aid Agency Data Breach…

Cyber Security News
KGB RAT Malware Bypasses Windows Defender to Steal Credentials and Control PCs
Cyber Security News7:52 AM

A Windows remote access trojan called KGB RAT gives attackers a way to spy on infected computers, collect credentials and control a victim’s desktop. The malware is sold as a service and advertised with a “fully undetectable” crypter that its sellers claim can bypass Windows Defender and other antivirus products. That claim should be treated […] The post KGB RAT Malware Bypasses Windows Defender…

Cyber Security News
Critical Next.js Vulnerabilities Allow Hackers to Execute Malicious Code Remotely
Cyber Security News7:39 AM

Next.js has released security updates for two critical vulnerabilities that could let remote attackers run malicious code without logging in. A third, high-severity flaw could stop affected applications from serving requests. The issues involve cached functions, SVG image processing, and Server Actions, with fixes available in Next.js 16.4.1 and 15.5.28. Published on October 14, 2026, […] The…

The Hacker News
Next.js Ships Out-of-Band Patch for Two Critical RCE Flaws in Caching and SVG Processing
The Hacker News7:28 AM

Next.js released an out-of-band security update on October 14 that fixes two critical flaws allowing unauthenticated remote code execution, along with a high-severity denial-of-service flaw. One code-execution flaw is in React Server Components, and the other in librsvg, the open-source library Next.js uses through the sharp package to handle SVG images. The fixes are in

The Hacker News
Drupal Patches Critical Field UI Flaw With Unauthenticated RCE Path via Contributed Modules
The Hacker News7:07 AM

Drupal core has a critical flaw in its Field UI module that could let an attacker run code on the site's server, and fixes were shipped on October 14 in Drupal 11.4.10, 11.3.19, and 10.6.19. An attacker cannot reach the flaw through core alone, the Drupal Security Team said in its advisory. Several exploit paths exist through contributed modules, and at least one known path needs no login.

BleepingComputer
Police arrests 95 suspects in international CSAM crackdown action
BleepingComputer6:55 AM

Law enforcement authorities from 17 countries in Latin America and Europe have arrested 95 suspects in an INTERPOL-coordinated operation targeting the distribution of child sexual abuse material (CSAM) through online messaging groups. [...]

The Hacker News
Fake AI Attacks Spread Across US Companies: How MSSPs Can Stop Incidents Early
The Hacker News6:46 AM

Attackers are impersonating popular AI products to distribute malware, steal browser sessions, and compromise business accounts. ANY.RUN linked 1,258 public sandbox analyses to fake AI campaigns between April and October of 2026.  The campaigns also increase operational pressure on MSSPs serving US businesses, which accounted for 16% of country-attributed targets.  Similar attacks

The Hacker News
Why AI Confidence Is Not Validation
The Hacker News6:04 AM

AI is already part of digital forensics and incident response work, with or without a policy in place to govern it. The issue is that these tools are growing more confident in their own output faster than practitioners are developing reliable ways to verify it. Without governance models and validation standards in place, that gap compounds and rarely stays contained to a workstation: an

Cyber Security News
CISA Warns of Hackers Exploiting Ivanti Connect Secure Zero-Day to Steal Credentials
Cyber Security News5:57 AM

CISA urged administrators to patch Ivanti Connect Secure appliances after attackers exploited CVE-2026-104935, a zero-day flaw that allows remote authentication bypass and command execution, enabling credential theft and data exfiltration. CISA issued its warning and added the flaw to its Known Exploited Vulnerabilities catalog on October 13, 2026. The warning covers Ivanti Connect Secure…

Cyber Security News
Microsoft Fixes Windows 11 Update Issue that Causes Black Screen Errors or Windows Explorer crash
Cyber Security News5:44 AM

Microsoft fixed a Windows 11 update issue that could leave users staring at a black screen after signing in or cause Windows Explorer to crash. The problem mainly affected Azure Virtual Desktop hosts using FSLogix, and some existing user profiles were more likely to fail to load the desktop. Microsoft marked the issue as resolved […] The post Microsoft Fixes Windows 11 Update Issue that Causes…
The Hacker News
India Mandates Registered Caller Name Display on 4G and Newer Networks From November 1
The Hacker News5:42 AM

The Indian government has directed telecom service providers (TSPs) in the country to mandatorily display callers' registered names along with their numbers for incoming calls starting November 1, 2026, in an effort to help people identify calls from unknown numbers and tackle spam or fraudulent calls. To that end, the Department of Telecommunications has issued a circular urging service

Cyber Security News
Ransomware Attacks Intensify: Criminals Shift Focus to Target Employees and Their Families
Cyber Security News5:28 AM

Ransomware gangs are moving beyond locked files and stolen data. Criminals now threaten employees, executives, and their families to force companies to pay. According to the Semperis 2026 Ransomware Risk Report, 37% of successful attacks included threats against workers’ friends or relatives. The findings show that ransomware is no longer only a technical crisis. It […] The post Ransomware…

Cyber Security News
Microsoft Windows Server 0-Day Flaw Lets Attackers Crash Servers With a Single Packet
Cyber Security News4:58 AM

Microsoft patched a Windows Server vulnerability that lets a network-adjacent attacker crash a server with a crafted Distributed File System (DFS) referral response. Tracked as CVE-2026-70111, the flaw affects Windows Server 2019, 2022, and 2025. Corelight researchers reported the issue after finding it while testing Microsoft Remote Procedure Call (MS-RPC) and DFS interfaces. The company […] The…

Cyber Security News
PoC Released for Critical Fortinet FortiClient EMS Authentication Bypass Vulnerability
Cyber Security News4:47 AM

A public proof-of-concept (PoC) for CVE-2026-35616, a critical authentication and authorization bypass in Fortinet FortiClient Endpoint Management Server (EMS), lets defenders test whether affected systems are exposed. The Python tool’s repository says the flaw can allow unauthenticated access to protected API endpoints. Fortinet has confirmed that the vulnerability was exploited in the wild…

Cyber Security News
Anthropic Warns AI Agents Can Now Automate the Entire Cyber Kill Chain
Cyber Security News4:27 AM

Anthropic has warned that attackers use AI agents to automate every stage of a cyberattack, from finding targets and stealing credentials to moving through networks and exfiltrating data. Its September 2026 threat report describes campaigns in which Claude became an active part of attack operations, rather than simply helping hackers write code. The findings cover […] The post Anthropic Warns AI…

Cyber Security News
UAT-6275 Hackers Exploit WinRAR Flaw to Target CIS Government Organizations
Cyber Security News4:08 AM

UAT-6275 hackers have used a known WinRAR flaw to plant malware on Windows systems while targeting government organizations across the Commonwealth of Independent States (CIS). The activity shows how an unpatched archive tool can turn a routine attachment into lasting remote access, with the malicious program starting when the victim next signs in. The campaign […] The post UAT-6275 Hackers…
The Hacker News
GhostAction Compromises About 1,900 GitHub Accounts, Targets Over 30,000 Repositories
The Hacker News3:45 AM

The credential-theft campaign known as GhostAction has ramped up, targeting more than 30,000 repositories across 3,000 users and organizations. The spike, according to GitGuardian, was observed on October 8 and 9, 2026. "This resulted from compromising the GitHub accounts of about 1,900 users. It attempted to extract 3,174 secrets from public repositories' CI," security researchers Gaetan

BleepingComputer
UK Legal Aid Agency: Hackers stole records dating back to 1978
BleepingComputer3:06 AM

The Legal Aid Agency (LAA), an executive agency of the UK's Ministry of Justice that manages the country's Public Defender Service, says attackers who breached its IT systems in April 2025 stole records dating back to 1978. [...]

Cyber Security News
Top 10 Best DLP Software in 2026 [Ranked & Scored]
Cyber Security News2:58 AM

DLP’s old reputation blocking legitimate work while real exfiltration walked out died with the pattern-only era. The 2026 winners judge context, ride enforcement points you already run, and explain every block. Microsoft Purview takes 1 on bundled reach; Netskope and Zscaler complete a SASE-heavy podium. Key Takeaways • 1 overall: Microsoft Purview DLP woven through […] The post Top 10 Best DLP…
Cyber Security News
Top 10 Best Malware Analysis Tools in 2026 [Ranked & Scored]
Cyber Security News2:11 AM

Every SOC question eventually becomes “what does this file actually do?” and the answer’s cost ranges from a free hash lookup to hypervisor-grade detonation. Evaluating detonation environments alongside the best malware sandbox tools for security teams and dynamic malware analysis tools demonstrates that modern adversaries actively design payloads with anti-evasion, sleep timers, and conditional…

The Hacker News
Langflow's Critical Authenticated RCE Flaw Targeted in 1,423 Honeypot Exploit Attempts
The Hacker News2:07 AM

Threat actors are exploiting a critical security flaw in Langflow, according to an alert from Previdian. Langflow is an open-source platform that allows developers to build artificial intelligence (AI) applications and agentic workflows. In February 2025, DataStax, the parent company of Langflow, was acquired by IBM. The vulnerability in question is CVE-2026-105740 (CVSS score: 9.9), a case of

Cyber Security News
Top 10 Best DevSecOps Platforms in 2026 [Ranked & Scored]
Cyber Security News2:02 AM

DevSecOps succeeds when security rides the pipeline instead of blocking it and fails when ten scanners produce ten backlogs nobody owns. Modern engineering teams aligning with enterprise DevSecOps playbooks recognize that vulnerability volume is a vanity metric; the true measure of a program is whether developers actually remediate what their tooling flags. We scored ten […] The post Top 10 Best…

The Hacker News
AhsayCBS Flaws Exploited to Deploy Web Shells Get New Fixes After Incomplete Patches
The Hacker News1:43 AM

Singapore-based Ahsay Backup has released security updates to address two security flaws in AhsayCBS that have been exploited by bad actors to drop web shells and XMRig cryptocurrency miners. The vulnerabilities in question are CVE-2026-105133 and CVE-2026-105134, which could be chained to sidestep authentication and execute arbitrary commands on affected systems. In a report published earlier

The Hacker News
Palo Alto Networks Patches PAN-OS Authenticated RCE Flaw Amid Active Exploitation
The Hacker News1:17 AM

Palo Alto Networks on Wednesday issued security updates for a high-severity flaw in PAN-OS software that has come under active exploitation. The vulnerability, tracked as CVE-2026-0322 (CVSS score: 8.6), is a case of remote code execution in the management interface. "A remote code execution (RCE) vulnerability in the management interface of Palo Alto Networks PAN-OS software enables an

Wednesday, October 14

Cyber Security News
Multiple Active Directory Vulnerabilities Let Attackers Bypass Security Feature Remotely
Cyber Security News10:51 PM

Microsoft has disclosed three Active Directory vulnerabilities that could let a remote attacker bypass a key security feature in Windows domain environments. The issues are tracked as CVE-2026-69982, CVE-2026-96252, and CVE-2026-108131, and administrators should review Microsoft’s Security Update Guide entries and deploy the available fixes as soon as possible. Active Directory is the central…

Cyber Security News
Hackers Exploit Palo Alto PAN-OS 0-day Flaw to Gain Root Code Execution on Firewalls
Cyber Security News10:42 PM

Hackers are exploiting a high-severity flaw in Palo Alto Networks PAN-OS that allows authenticated attackers to run code with root privileges on affected firewalls. Tracked as CVE-2026-0322, the vulnerability affects the management interface, with the company confirming “very limited exploitation” and urging customers to apply fixes as soon as possible. Palo Alto Networks published its […] The…

Cyber Security News
Cisco Secure Email Gateway 0-Day Vulnerability Actively Exploited in Attacks
Cyber Security News10:06 PM

Cisco has warned that attackers are actively exploiting a critical zero-day vulnerability in Cisco Secure Email Gateway that can give them root access to affected appliances. Tracked as CVE-2026-76519, the flaw carries a CVSS score of 9.8 and allows attacks through specially crafted email attachments without requiring a login. Cisco published its advisory on October […] The post Cisco Secure…

BleepingComputer
FBI raids DPRK IT worker laptop farms in Texas, US nationals arrested
BleepingComputer2:41 PM

The U.S. Department of Justice (DoJ) has disrupted the Famous Chollima threat group's operations by arresting two suspects, charging 14 individuals, and seizing nearly 187 laptops used in North Korean remote IT worker schemes. [...]

The Hacker News
Cisco Warns of Active Attacks Exploiting New Critical Secure Email Gateway Vulnerability
The Hacker News1:38 PM

Attackers are exploiting a critical flaw in Cisco Secure Email Gateway that lets a sender with no login write files to the appliance's operating system, Cisco said in an advisory on Wednesday. The attacker sends an email with a crafted attachment through the gateway and, if it succeeds, could then run commands as root. The appliance filters an organization's email for spam, malware,

Cyber Security News
Multiple NGINX Flaws Let Remote Attackers Crash Servers and Execute Malicious Code
Cyber Security News1:19 PM

F5 has disclosed three serious security flaws in NGINX Plus and NGINX Open Source that can let remote, unauthenticated attackers crash worker processes by sending crafted HTTP requests. In certain setups, the memory errors could also allow code execution, although F5 says that outcome requires Address Space Layout Randomization, known as ASLR, to be disabled […] The post Multiple NGINX Flaws Let…

BleepingComputer
Ledger asks sellers across Asia to halt sales after supply-chain attack
BleepingComputer12:46 PM

Ledger has asked resellers and distributors of its wallets in Indonesia, Singapore, Thailand, the Philippines, Vietnam, Malaysia, and Hong Kong to suspend device sales and remove products from shelves while it investigates device tampering. [...]

The Hacker News
Hackers Backdoor Nextcloud Servers Through Critical Flaw in Collabora’s Built-in CODE App
The Hacker News12:38 PM

Attackers exploited a flaw in an optional Nextcloud app, Collabora Online - Built-in CODE Server, to plant web shells on Nextcloud servers. Three administrators reported the issue on GitHub, with the first logged attack on September 10. A web shell is a small file that executes any command an attacker sends via a web request, with the rights of the web server account. The flaw

The Hacker News
Microsoft Disrupts 3 Phishing Kits Linked to Over 1 Billion Scam Messages
The Hacker News12:09 PM

Microsoft and Health-ISAC, along with the Japan Cybercrime Control Center (JC3) and a coalition of private sector companies, such as Resecurity, Cloudflare, Oracle, Proofpoint, and TRM Labs, announced the disruption of three phishing kits, CoGUI (aka NX or FA), Haozi (aka Phoenix), and Iron Man System. "Since January 2026, the threat actors behind these kits have been responsible for

Cyber Security News
24 Security Vulnerabilities Patched in curl Used Across 30 Billion Installations
Cyber Security News11:46 AM

The curl project released curl 8.23.0 on October 14, 2026, announcing 24 security fixes affecting the widely used data transfer tool and its underlying library, libcurl. The vulnerabilities include credential leaks, authentication errors, command injection, and flaws that can disrupt applications. The release also removes SMB and SMBS protocol support, making compatibility checks important before…

The Hacker News
U.S. Shuts Down Over 40 Laptop Farms, Charges 14 in North Korean IT Worker Fraud
The Hacker News11:34 AM

The U.S. Department of Justice (DoJ) on Tuesday charged 14 people and seized about 187 computers as part of its ongoing efforts to disrupt North Korea's fraudulent remote IT worker (ITW) scheme. The indictment charges a mix of U.S. citizens and Chinese nationals for their roles in an IT worker conspiracy affecting more than 70 U.S. companies, charging them with wire fraud conspiracy, money

Cyber Security News
How MSSPs Can Cut Tier 1 Bottlenecks Eating into Profit Margins
Cyber Security News11:29 AM

As MSSPs take on more clients, alert volumes grow fast. Analyst capacity usually doesn’t. That gap shows up in triage and response first. Teams spend too much time checking IOCs, switching between tools, rebuilding context, and escalating cases that could have been closed earlier. Across thousands of investigations, those extra minutes turn into slower response, more […] The post How MSSPs Can…

Schneier on Security
Upcoming Speaking Engagements
Schneier on Security11:02 AM

This is a current list of where and when I am scheduled to speak: I’m speaking at ATTENTION: Democracy, Rebuilt in Montreal, Canada. The event runs October 21–23, 2026, and my talk is on Wednesday, October 21. I’m speaking at the University of Toronto in Toronto, Ontario, Canada, at 5 PM ET on October 22, 2026. I’m speaking at [un]prompted in San Francisco, California. The event runs October…

Cyber Security News
Microsoft’s Recent Windows Updates Break Remote Desktop Services With Error “0xC000000D”
Cyber Security News10:51 AM

Microsoft has confirmed a Windows 11 Remote Desktop issue that can prevent non-admin users from connecting to remote computers with Administrator protection enabled. The problem follows the September 22, 2026, non-security preview update, KB5124010, or later updates. It mainly affects company-managed computers used as Remote Desktop hosts. Failed connections may return error 0xC000000D and…

Schneier on Security
The Future of AI Cryptanalysis
Schneier on Security9:24 AM

Matthew Green has been writing a rather pessimistic series of posts about the potential for AI systems to vastly outperform humans in cryptanalysis of both symmetric and public-key ciphers. I am more optimistic than he is. That is, I have stronger faith in the over-engineering cryptographers tend to do. I am trying to write this up in more detail.

Krebs on Security
U.K. Sanctions Cryptomus for RU Money Laundering
Krebs on Security9:22 AM

The United Kingdom has issued economic sanctions against Cryptomus, a chameleonic cryptocurrency platform that experts say serves as a major conduit for payments related to ransomware, narcotics, darknet markets, fraud and cybercrime services that are helping Russia circumvent existing financial restrictions.

Schneier on Security
Cyberattack on Connected Fridges in France
Schneier on Security9:10 AM

Another IoT cyberattack , this one in France: Hackers gained control of the software that regulates the temperatures of the refrigeration units, forcing some to warm to 50C (120F) overnight, according to one supermarket chain affected. […] Normally, supermarket freezers go through a short period of defrosting overnight, in which temperatures rise slightly. But the hackers ordered the units to…

Cyber Security News
Hackers Use Fake WatchGuard VPN Download Site to Steal Login Credentials
Cyber Security News9:08 AM

Hackers used a fake WatchGuard VPN download website to steal login details before offering visitors the real, digitally signed VPN installer. The attack collected a VPN server address, username, and password through a browser pop-up, leaving victims exposed without installing a malicious client. The campaign shows how a normal software search can lead to credential […] The post Hackers Use Fake…

BleepingComputer
The Blind Spots of Agentic Pentesting and How to Close Them
BleepingComputer9:00 AM

AI-powered penetration testing can uncover complex attack paths, but safety restrictions and network limitations leave many assets and vulnerabilities untested. Picus Security explains how combining agentic pentesting with exposure validation and breach simulation can help close these gaps. [...]

Cyber Security News
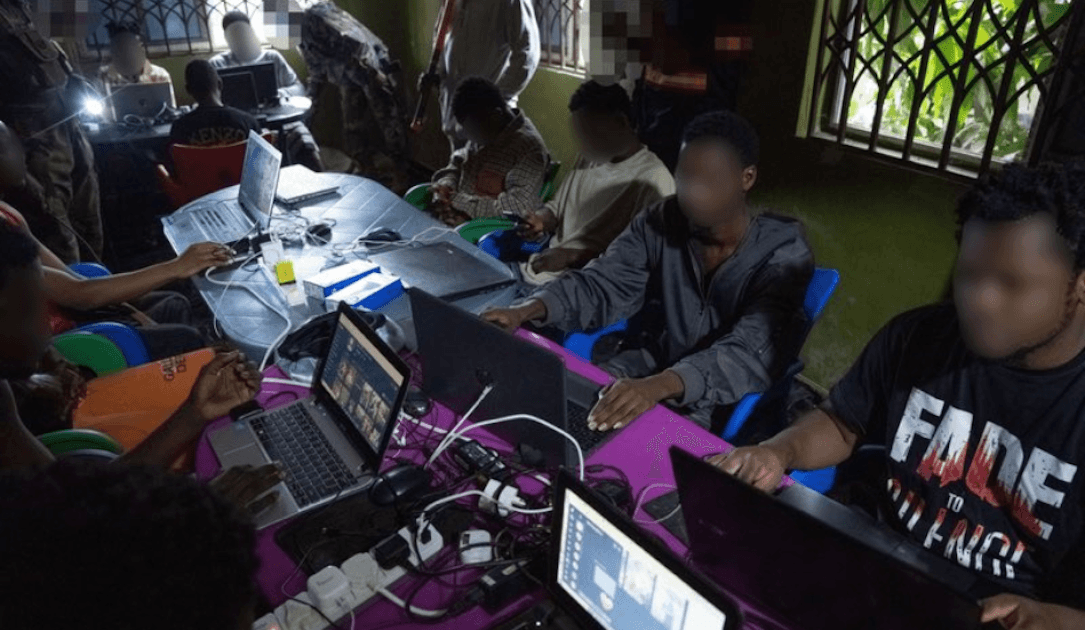
Meta, Google, Microsoft and OpenAI Join Global Crackdown on West African Scam Networks
Cyber Security News8:44 AM

Meta, Google, Microsoft and OpenAI joined an international crackdown on West African scam networks that removed more than 3.7 million Facebook and Instagram accounts, pages and groups. Announced on October 13, 2026, the operation led to 28 arrests and the rescue of 117 people forced to work inside scam centers. The United Kingdom’s National Crime […] The post Meta, Google, Microsoft and OpenAI…

Cyber Security News
PoC Released for Linux Vhost Flaw Enabling Root Privilege Escalation and VM Escape
Cyber Security News8:19 AM

A public proof of concept for Vghost, a high-severity Linux vhost flaw tracked as CVE-2026-74580, shows how the bug can let a local user gain root access or, in certain virtual machine setups, break out of a guest and affect the host. The issue has a CVSS v3.1 score of 8.8 and is fixed in […] The post PoC Released for Linux Vhost Flaw Enabling Root Privilege Escalation and VM Escape appeared…

BleepingComputer
Global takedown hits network behind 1 billion phishing messages
BleepingComputer8:12 AM

A massive cybercriminal ecosystem facilitating more than a billion malicious messages targeting over 75,000 organizations across 150 countries has been disrupted by law enforcement agencies and partners worldwide. [...]

Cyber Security News
FBI Disrupts North Korean Famous Chollima Laptop Farms Used to Infiltrate U.S. Companies
Cyber Security News7:37 AM

The FBI disrupted several U.S. laptop farms used by North Korean threat group FAMOUS CHOLLIMA in late September 2026, cutting off infrastructure that helped fake remote workers enter American companies. CrowdStrike disclosed the joint operation on October 13, describing it as the start of a wider effort against the group’s domestic support network. The farms […] The post FBI Disrupts North Korean…

The Hacker News
CISA Urges Immediate Ivanti Connect Secure Updates as Honeypots Log 105 Exploit Attempts
The Hacker News7:30 AM

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Tuesday urged organizations to take steps to immediately update their Ivanti Connect Secure (ICS) appliances and deployments to the latest version following the disclosure of an actively exploited vulnerability. The security flaw, tracked as CVE-2026-104935 (CVSS score: 8.6), is a case of authentication bypass impacting ICS

The Hacker News
curl Patches HTTP/2 Upload Flaw After PoC Demonstrates Client-Side Code Execution
The Hacker News7:13 AM

A flaw in how curl handles HTTP/2 uploads lets a malicious server receiving an upload corrupt the client's memory, and the researcher who reported it turned that into code execution on the uploading machine. The curl project fixed it on October 14 in curl 8.23.0. Taking over a client needs exact knowledge of its build and memory layout, and curl expects a real attack to end in a crash

The Hacker News
How to Run a Deepfake Readiness Drill Before a Cloned Voice Calls Your Team
The Hacker News6:50 AM

Cloned voices and synthetic video calls now show up in payment fraud, help desk resets, and access requests. A structured drill shows security teams exactly where verification breaks down, while nothing is at stake. The call comes in at 4:40 on a Friday. It's the CFO, or it sounds exactly like her, asking the controller to push a supplier payment out before the weekend because a deal closes

The Hacker News
Researchers Used a Public OpenAI Model to Build a $250,000 Chrome Full-Chain Exploit in Six Days
The Hacker News6:19 AM

A team at security firm XBOW chained three then-unknown Google Chrome bugs into a single attack that runs code on a Windows computer when the user only loads a web page, the company said. Its researchers built the attack in six days by directing AI agents running OpenAI's publicly available GPT-5.6 Sol model. Google has since confirmed all three bugs, fixed them, and paid XBOW its top $

The Hacker News
Hirudo Android Trojan Uses Patched Banking Apps to Bypass Their Built-In Security Checks
The Hacker News6:08 AM

Cybersecurity researchers have disclosed details of a new Android banking trojan called Hirudo that works by replacing legitimate banking apps with purpose-built patched versions designed to bypass security checks from inside the app itself, marking a new escalation in financial fraud.  Dutch mobile security company ThreatFabric said it identified replacements for eight Indonesian banking

The Hacker News
An AI Agent Found a Critical OTP Bypass in Production. The Attack Was the Easy Part.
The Hacker News6:00 AM

The bug was simple: the login let you choose where your sign-in code went. Proving it on a live website was the hard part. TL;DR During an authorized assessment, an AI pentesting agent found a critical authentication bypass on a major insurer's production website, on its own. One login request let the user choose where the one-time passcode went. The attack was the easy part. Proving it

Cyber Security News
VirusTotal Integrates Threat Intelligence With ChatGPT for Malware Analysis
Cyber Security News5:45 AM

VirusTotal can now bring threat intelligence into ChatGPT through VirusTotal AI (VTAI), allowing users to investigate suspicious files, URLs, domains, and IP addresses within a conversation. The connection helps analysts retrieve existing reports and explain detection results while keeping the source, analysis date, and coverage visible. The integration uses Model Context Protocol (MCP), a…

Cyber Security News
Google Awarded $250,000 Bounty for a Full-chain Chrome Exploit Found Using GPT-5.6
Cyber Security News4:37 AM

Security researchers earned a $250,000 reward from Google after building a full-chain Chrome exploit with AI agents. The XBOW team says the work took six days and about $40,000 in computing costs, using OpenAI’s publicly available GPT-5.6 Sol model. Google has fixed the flaws. XBOW disclosed the work on October 13, 2026. Its chain linked […] The post Google Awarded $250,000 Bounty for a…

Cyber Security News
Windows SmartScreen Vulnerability Enables Privilege Escalation Attacks
Cyber Security News4:28 AM

Microsoft has released fixes for a Windows SmartScreen vulnerability that allows an attacker with local access to gain higher privileges. Tracked as CVE-2026-85851, the flaw was disclosed on October 13, 2026, and carries a CVSS base score of 7.8. Microsoft rates it Important. The issue involves a use-after-free memory error and affects several Windows 11 […] The post Windows SmartScreen…

Cyber Security News
Coruna and DarkSword Exploit Kits Can Fully Compromise iPhones From a Single Web Visit
Cyber Security News4:26 AM

Two powerful iPhone exploit kits, Coruna and DarkSword, show how a visit to a malicious or compromised website can put an outdated device at risk. The kits can link several software flaws together to break out of the browser and reach deeper parts of iOS. Depending on the device’s software version and the kit used, […] The post Coruna and DarkSword Exploit Kits Can Fully Compromise iPhones From a…

Cyber Security News
Hackers Breach Meta GitHub Repositories, Steal Source Code and Data of 1,500 People
Cyber Security News3:49 AM

Hackers used an employee’s stolen credentials to access some of Meta’s GitHub repositories, taking product source code and personal information linked to roughly 1,500 people. Most affected individuals are Meta employees in the United States, according to the company’s disclosure to SecurityWeek. Meta confirmed the breach on October 13, 2026, when it began notifying affected […] The post Hackers…

Cyber Security News
Attackers Breach European Bank Through Third-Party Gateway and Target WSUS Server
Cyber Security News3:33 AM

A European bank was breached through a poorly secured, third-party gateway before an attacker tried to exploit its Windows Server Update Services (WSUS) infrastructure. The case shows how stolen login details and weak access controls can put a bank’s central software systems at risk without a complex attack chain. The bank’s security team uncovered unauthorized […] The post Attackers Breach…
Cyber Security News
Gears of War: E-Day Hit by DDoS Attack, Causing Login Failures and Disconnects
Cyber Security News3:11 AM

Gear of War: E-Day players faced login failures, sudden disconnects, and other online service problems after distributed denial-of-service attacks targeted the game’s online services. The official Gears Community account confirmed the cause on X, linking the disruption to DDoS activity and ending speculation about the source of the failures. The Gears Community reported attacks on […] The post…

Cyber Security News
Multiple Google Chrome Flaws Could Enable Memory Corruption and Code Execution Attacks
Cyber Security News2:59 AM

Google released a Chrome security update that addresses 37 vulnerabilities, including seven critical flaws that raise concerns about memory corruption and possible code execution. Published on October 13, 2026, the update covers Windows, Mac, and Linux, with fixes spanning graphics, PDF handling, media processing, networking, and other browser components. According to Google’s Stable Channel…

Cyber Security News
Ivanti Connect Secure 0-Days Exploited to Steal Active Directory Credentials
Cyber Security News2:51 AM

Attackers chained three zero-day flaws in Ivanti Connect Secure VPN appliances to gain root-level access without logging in, then searched for credentials and sensitive Active Directory data. The activity, which began on October 3, 2026, targeted a fully patched appliance running version 22.8R2.4, showing that keeping a device current did not protect it from these […] The post Ivanti Connect…

The Hacker News
AI-Found Linux Kernel Flaw Gives Local Users Root, and Can Break a Guest Out to the Host
The Hacker News2:46 AM

A flaw in Linux's vhost subsystem lets a local user read and write kernel memory at will and become root across nearly a decade of kernel versions. In one virtualization setup, it lets an untrusted virtual machine write to the host's memory and hijack the program that runs the virtual machine. The bug is tracked as CVE-2026-74580 and named Vghost. Tencent Zhuque Lab, which found the

Cyber Security News
Windows BitLocker Vulnerabilities Security Feature Bypass and Privilege Elevation Attacks
Cyber Security News2:03 AM

Microsoft fixed three Windows BitLocker vulnerabilities CVE-2026-85920, CVE-2026-88070, and CVE-2026-83500 that could enable privilege escalation or bypass security protections in its October 2026 updates. BitLocker is a core Windows disk-encryption feature designed to protect data if a laptop, desktop, or storage drive is lost or stolen. It helps prevent someone from reading protected files by…

The Hacker News
Four-Byte Write and Timing Bug Let Researchers Run Code in Windows SmartScreen Enclave
The Hacker News12:52 AM

Security researchers ran their own code inside a protected part of Windows that is meant to stay sealed off even when the rest of the computer is taken over. The protected area is a VBS enclave, an isolated slice of memory the operating system uses to guard secrets, and the one they broke into handles passwords for a Windows anti-phishing feature. The work was done in a lab as a proof of

Tuesday, October 13

The Hacker News
Microsoft Patches Record 1,413 Flaws, Including Exploited Windows Shell Bug
The Hacker News11:34 PM

Microsoft on Tuesday shattered its own Patch Tuesday record by shipping patches for a whopping 1,413 vulnerabilities, including one that it said has come under active exploitation. These include 1,102 flaws in Windows, 134 in Office, 61 in Developer Tools, 36 in SharePoint Server, and 22 in SQL Server. Of these, more than 670 relate to privilege escalation, followed by over 300 remote code

Cyber Security News
Microsoft Windows Shell 0-Day Vulnerability Actively Exploited in Attacks
Cyber Security News10:28 PM

Microsoft has patched an actively exploited Windows Shell zero-day vulnerability that allows attackers to bypass Mark of the Web protections. Tracked as CVE-2026-96951, the flaw was addressed in the October 2026 Patch Tuesday updates. It carries a CVSS score of 8.8 and is rated Important by Microsoft. The vulnerability was not publicly disclosed before the […] The post Microsoft Windows Shell…

Cyber Security News
OpenAI Engineer Arrested for Planting Spyware Device in an Executive Conference Room
Cyber Security News9:25 PM

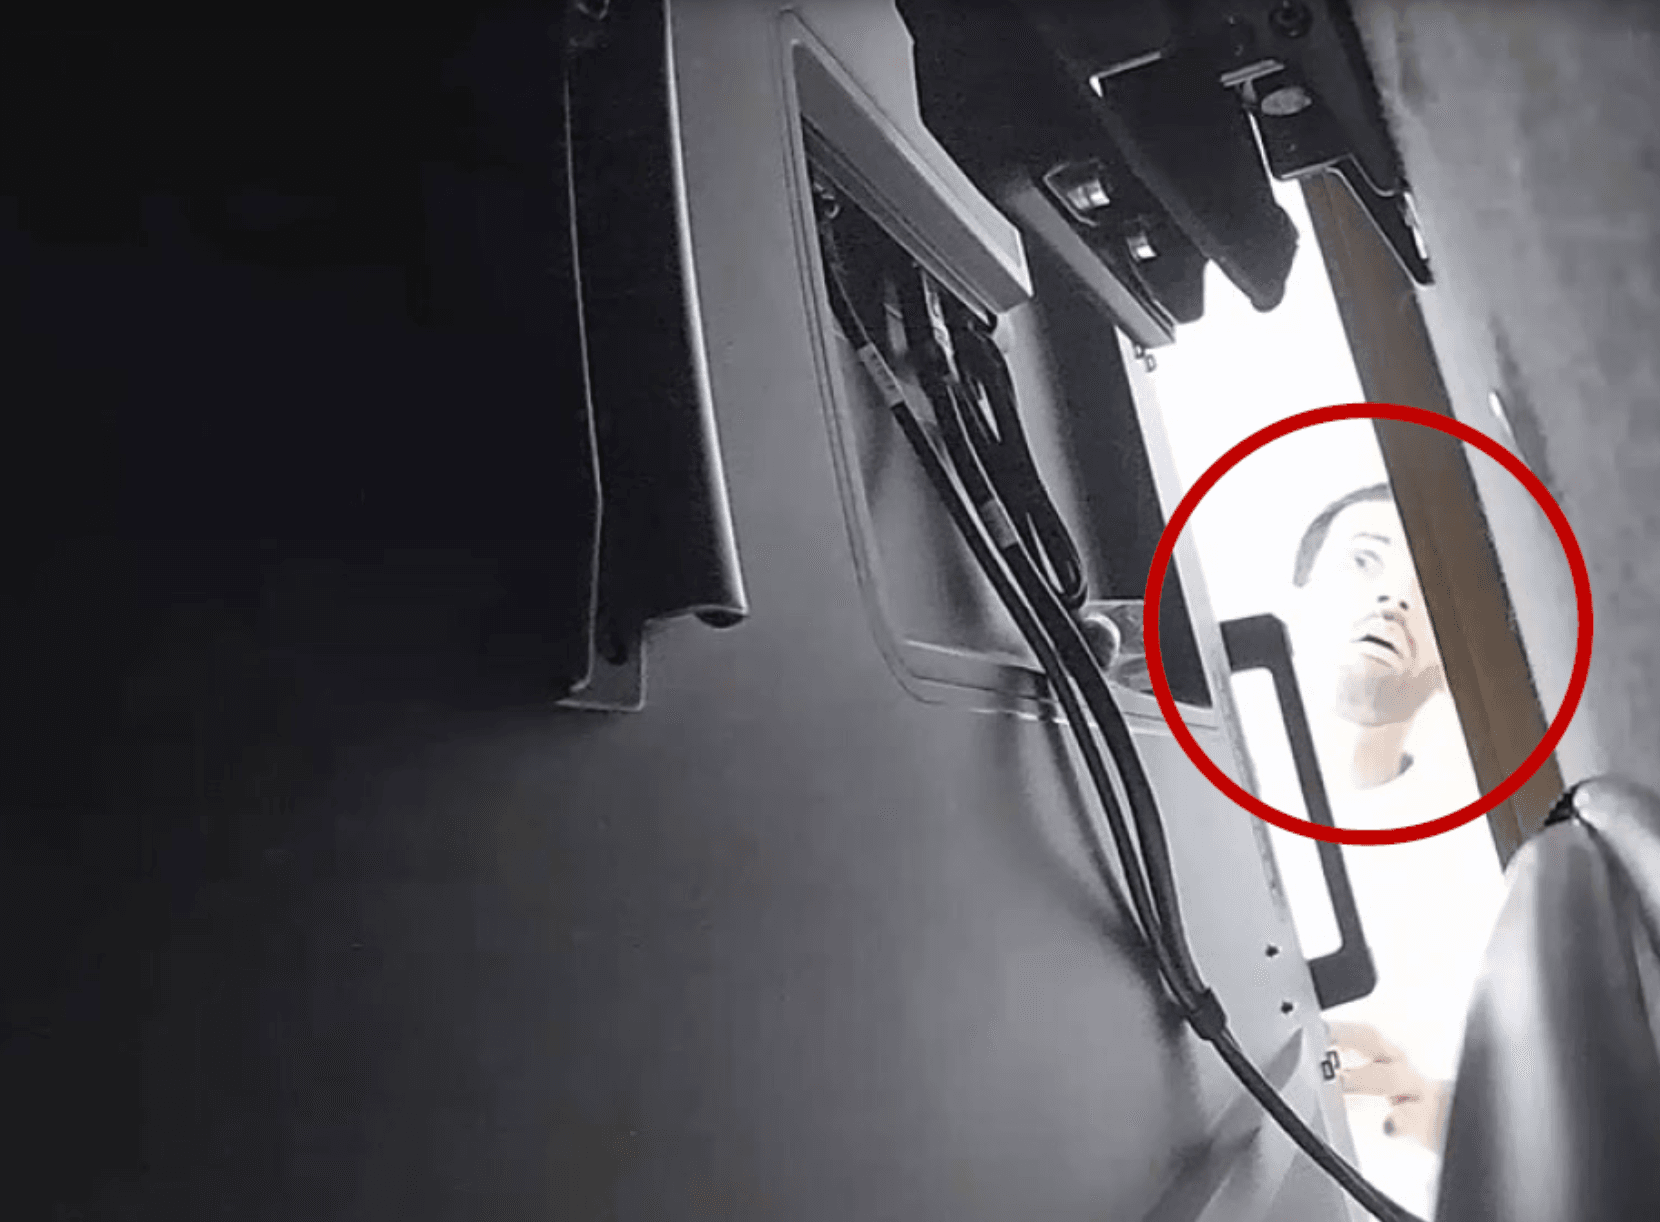
An OpenAI engineer has been arrested for allegedly hiding an audio recording device in an executive conference room at the company’s San Francisco offices. Abdulrahman Alfozan, 35, a Saudi national, was arrested on October 9, 2026, and appeared in federal court on October 13, according to the U.S. Department of Justice. Prosecutors charged him with […] The post OpenAI Engineer Arrested for…

The Hacker News
OpenAI Employee Arrested for Allegedly Planting Hidden Recorder in Executive Conference Room
The Hacker News8:59 PM

A Saudi National and employee of OpenAI has been arrested for allegedly planting a hidden recording device in an executive conference room at the company's San Francisco offices to covertly record sensitive conversations. Abdulrahman Alfozan, 35, has been charged with using or endeavoring to use an electronic, mechanical, or other device to intercept oral communications. He was arrested by

Krebs on Security
Microsoft Patches More Than 1,400 Security Flaws
Krebs on Security6:24 PM

Microsoft today issued updates to fix more than 1,400 security vulnerabilities in its Windows operating systems and other software. Today's epic patch batch dwarfs September's record of nearly 1,000 fixes, which was already about ten times the normal monthly patch load from Redmond.

Dark Reading
North Korea Phishes Ukrainians for War Intel
Dark Reading4:24 PM

The Democratic People's Republic of Korea (DPRK) is trying to get insight into its own war effort in Ukraine, through simple reply-baiting phishing attacks.

BleepingComputer
Anthropic warns self-replicating AI could spread to your smart devices
BleepingComputer4:16 PM

Anthropic is warning that small AI models could soon be able to self-replicate across consumer IoT devices, from Android TV boxes to smart ovens, creating distributed botnets capable of running AI workloads without relying on data centers. [...]

SANS Internet Storm Center
October 2026 Microsoft Patch Tuesday, (Tue, Oct 13th)
SANS Internet Storm Center2:25 PM

Microsoft today released patches for 1,417 vulnerabilities. 76 of these vulnerabilities are rated critical, with 7 critical vulnerabiilties requiring no customer actions. One vulnerability was disclosed before today&#;x26;#;39;s patch Tuesday, and one is already exploited.

The Hacker News
Anthropic Warns Small AI Models Could Soon Form Self-Propagating IoT Botnets
The Hacker News1:20 PM

Small artificial intelligence (AI) models may be months away from developing capabilities to self-replicate on IoT devices like smart ovens and off-brand Android TV boxes, according to a warning from Anthropic. The frontier AI lab said small AI models could form autonomous, self-propagating worm botnets that are "challenging to shut down," since "there's no centralized point to shut off."

Cyber Security News
Microsoft Fixes 1,118 Vulnerabilities in October Patch Tuesday and Introduces New Risk Cohorts
Cyber Security News1:19 PM

Microsoft’s October 2026 Patch Tuesday briefing outlines 1,118 vulnerabilities across 15 risk groups, alongside a new approach designed to help security teams review large update releases. Called risk cohorts, these groups bring together flaws that require similar questions about an organization’s systems, users, and exposure. Microsoft’s accompanying document maps individual CVEs to these shared…

The Hacker News
Docker Fixes Critical Two-Year-Old Hub Flaw That Let One User Push Images as Another
The Hacker News1:03 PM

A flaw in Docker Hub, the registry where container images are published and downloaded, let one user push, pull, or delete images as another user. Docker fixed the flaw on September 30 and says it found no evidence that anyone exploited it. The flaw was in the feature that converts a personal account into an organization, Docker said in a security advisory on October 12.

Cyber Security News
Critical FortiSandbox GUI Vulnerability Allows Remote Attackers to Bypass Authentication
Cyber Security News12:54 PM

Fortinet disclosed a critical authentication-bypass vulnerability in the FortiSandbox graphical user interface that could let remote attackers access protected functions without valid credentials. Tracked as CVE-2026-107656, the flaw carries a reported CVSSv3 score of 9.6 and affects both FortiSandbox appliances and selected FortiSandbox PaaS releases. Published on October 13, 2026, the…

BleepingComputer
Windows 11 KB5127648 & KB5126653 cumulative updates released
BleepingComputer12:49 PM

Microsoft has released the Patch Tuesday Windows 11 KB5127648 and KB5126653 cumulative updates for versions 26H2/25H2/24H2 and 23H2 to fix security vulnerabilities and bugs, and add new features. [...]

The Hacker News
Attacker Chains Three Ivanti Connect Secure Zero-Days for Root Access, Only Two Patched So Far
The Hacker News12:33 PM

An attacker chained three zero-day flaws in Ivanti Connect Secure, a VPN appliance, to run commands as root without logging in, security firm Volexity said on October 13. Ivanti has released fixes for two of the flaws and told customers on affected versions to "act immediately." A fix for the third is still pending, according to Volexity. Volexity, which reported the flaws to Ivanti,

The Hacker News
SAP Discloses Critical CVSS 10 Flaw in Cloud SDK for Python Allowing OAuth2 Credential Theft
The Hacker News12:28 PM

A flaw in SAP's Cloud SDK for Python can send an application's OAuth2 client credentials to a server an attacker controls, SAP said in a security advisory on October 13. The flaw affects multi-tenant applications on SAP Business Technology Platform (BTP) that use the SDK, SAP's official Python client for BTP services. An attacker must be able to control the tenant subdomain,

Cyber Security News
TFG London Cyberattack Disrupts IT Systems Used by Phase Eight, Hobbs, and Whistles Brands
Cyber Security News12:26 PM

TFG London has confirmed a cyberattack that disrupted IT systems supporting Phase Eight, Hobbs, and Whistles. South Africa’s The Foschini Group detected the incident on October 11, 2026, and disclosed it to shareholders on October 13. Several systems remained unavailable, although stores continued trading. According to the company’s shareholder announcement, Inside Story and White Stuff […] The…

Cyber Security News
Critical Docker Hub Flaw Lets Attackers Impersonate Users and Push Container Images
Cyber Security News11:55 AM

Docker has disclosed a critical Docker Hub vulnerability that could let attackers impersonate other users and publish container images under trusted names. Tracked as CVE-2026-105445, the flaw affected personal access tokens transferred during account conversions. Docker resolved the issue on September 30, 2026, stating its investigation found no evidence of exploitation. This issue posed a […]…

Cyber Security News
CrowdStrike Joins Anthropic Defense Program to Advance AI-powered Defense for Critical Infrastructure
Cyber Security News11:49 AM

CrowdStrike has joined Anthropic’s Critical Infrastructure Defense Program to help strengthen AI-powered cybersecurity across energy, water, manufacturing, and transportation systems. Announced on October 8, 2026, the partnership combines CrowdStrike’s experience protecting business and industrial networks with Anthropic’s advanced Claude models, technical support, and cybersecurity research. The…

The Hacker News
GitHub Tightens npm Publishing After Flaw Left 1,500+ Packages Vulnerable to Hijacking
The Hacker News11:18 AM

GitHub has taken the step of expiring unvalidated npm trusted publishing configurations 48 hours after creation after researchers found that it was possible for an attacker to push new versions of a different user's package without having to steal their credentials. "Your configuration becomes validated and exempt from expiry after its first successful publish," the Microsoft-owned subsidiary

Cyber Security News
Zoom Clients for Certificate Validation Flaw Exposes Sensitive Information via Network Access
Cyber Security News11:15 AM

Two high-severity certificate validation flaws in Zoom clients could allow attackers without login credentials to access sensitive information over a network, according to advisory text dated October 13, 2026. The issues affect Windows clients and the My Notes feature across desktop and mobile platforms, making updates important for both personal users and business deployments. The […] The post…

Cyber Security News
Ivanti Connect Secure 0-Day Vulnerability Actively Exploited in the Wild
Cyber Security News10:55 AM

Ivanti has disclosed an actively exploited zero-day vulnerability in Ivanti Connect Secure (ICS) that allows remote attackers to execute arbitrary commands without logging in. Tracked as CVE-2026-104935, the flaw carries a high-severity CVSS score of 8.6. Ivanti confirmed that exploitation affected a limited number of customers in its October 13, 2026 advisory. The vulnerability involves […] The…

Cyber Security News
Danfoss Refrigeration Hack Update – 4,980 Hosts Found Exposed to Internet
Cyber Security News10:49 AM

France accounts for more than half of the internet-facing hosts found in a Shodan search for Danfoss web pages, following a cyberattack that disrupted supermarket refrigeration systems. An update from International Cyber Digest on October 13 reports a total of 4,980 hosts identified, with 2,911 located in France and 517 in South Africa. These findings […] The post Danfoss Refrigeration Hack…

Cyber Security News
CISA Warns of Hackers Exploiting Two Citrix NetScaler 0-Days to Execute Code Remotely
Cyber Security News10:26 AM

Threat actors are actively exploiting two critical zero-day vulnerabilities in Citrix NetScaler ADC and NetScaler Gateway appliances, allowing them to execute code remotely on exposed systems. The flaws, tracked as CVE-2026-88771 and CVE-2026-88772, received a CVSS v4 severity score of 9.5 out of 10 and have been added to the U.S. Cybersecurity and Infrastructure Security […] The post CISA Warns…

Cyber Security News
Threat Intelligence Guide for US SOC Teams and CISOs: How to Choose the Right Solution
Cyber Security News10:02 AM

Choosing an enterprise threat intelligence solution is about more than just data volume or integrations. The right provider should deliver relevant intelligence, fit existing workflows, and help security teams investigate threats faster.  While SOCs may prioritize rapid investigation and enrichment at scale, MSSPs may focus more on multi-tenancy and customer separation.  This enterprise threat…

BleepingComputer
The MFA Gaps Attackers are Still Exploiting
BleepingComputer9:01 AM

Attackers continue exploiting gaps in MFA coverage, using stolen credentials to access VPNs, RDP, and Windows systems that still rely on passwords alone. Specops explains why protecting cloud applications isn't enough and how organizations can close these authentication gaps. [...]

Cyber Security News
Criminal IP to Showcase Threat Intelligence and AITEM at Security Days Fall 2026 Tokyo
Cyber Security News8:57 AM

Torrance, California, October 13th, 2026, CyberNewswire Criminal IP, developed by AI SPERA, will participate in Security Days Fall 2026 Tokyo, taking place October 21–23, 2026, at the TAKANAWA GATEWAY Convention Center. At booth B20, Criminal IP will showcase Criminal IP Threat Intelligence (Criminal IP TI) and Criminal IP AITEM (AI-Powered Threat Exposure Management) through live […] The post…

Cyber Security News
G2A.COM Reports 35% Growth in Security Software Orders, Outpacing VPN Growth
Cyber Security News8:56 AM

Amsterdam, Netherlands, October 13th, 2026, CyberNewswire Antivirus and security software orders grow more than twice as fast as VPN orders, accounting for 43% of cybersecurity purchases on the marketplace  G2A.COM, a digital marketplace that serves more than 35 million users across 180 countries, reports a 35% year-on-year surge in antivirus and security software orders, outpacing […] The post…

BleepingComputer
SAP warns of maximum severity OAuth2 SSRF security flaw
BleepingComputer8:51 AM

SAP has addressed 20 security flaws across multiple products in its October 2026 security updates, including a maximum-severity vulnerability in the Cloud SDK for Python. [...]

The Hacker News
Xandr Fined a Record €8.6 Million for Relaying Grindr Data Revealing Sexual Orientation
The Hacker News8:12 AM

The Norwegian Data Protection Authority (DPA) has fined Xandr, an advertising unit owned by Microsoft, €8.6 million ($9.62 million) for illegally relaying ​Grindr users' sensitive data to advertisers. The administrative penalty is the largest issued by the data protection watchdog, arguing the case merited a high fine because of the "very serious" nature of the breach. The infringements

The Hacker News
[Webinar] How to Stop AI-Driven Privilege Escalation With Runtime Identity Controls
The Hacker News6:57 AM

The dangerous part of a stolen identity isn't always the initial login. It's what an attacker can do with that access next. With AI accelerating reconnaissance, exploitation of vulnerabilities, and privilege escalation, attackers can move through systems faster than security teams can investigate. A compromised account that looks legitimate at first could become the starting point for a much

The Hacker News
LG Smart TVs Vulnerable to Pre-Auth Root Takeover From Local Network
The Hacker News6:09 AM

Three vulnerabilities in LG's webOS can be chained to give an attacker on the same local network root access to certain smart TVs without a PIN or any interaction from the owner. LG has issued a fix, according to an advisory published by SSD Secure Disclosure on October 12. The chain was tested on two TV models, the 32LQ636BPSA and the 27TQ600SW, running webOS 7.5.7-25 on firmware

The Hacker News
Product Walkthrough: Bitdefender AI Visibility and Control
The Hacker News5:30 AM

A user opens a browser tab, pastes data into a chat assistant, and nothing is installed. A developer adds a coding assistant as an editor extension, and nothing shows up in the installed programs list. Someone downloads a local model runtime, a program that runs models directly on the machine instead of sending data to an external service, because they were told not to send company data

r/netsec
Playing It SFAPE: Code Execution in Isolated User Mode
r/netsec4:25 AM

Doyensec discovered multiple vulnerabilities in SFAPE.dll , a VBS enclave shipped with Windows, and chained them to gain code execution within the enclave in Windows Isolated User Mode (VTL1). The post explores how VBS enclaves work and how memory corruption can undermine their isolation guarantees. Microsoft addressed the reported issue in the September 2026 bulletin under CVE-2026-83498 .

The Hacker News
Attackers Heat French Supermarket Fridges Up to 50°C by Hijacking Danfoss Controllers
The Hacker News3:48 AM

Attackers took remote control of fridges and freezers at hundreds of French supermarkets on the night of October 11 and warmed them, forcing stores to throw food away, several retail chains said. The attackers reached them through the controller that runs all of a store's fridges and freezers, a device made by Danish company Danfoss that maintenance firms can manage remotely. Les Mousquetaires

The Hacker News
Two Critical MarkLogic Flaws Could Give Delegated Managers Persistent Admin Control
The Hacker News3:44 AM

Two of 31 newly disclosed flaws in Progress Software's MarkLogic Server database could let an account given only some management privileges take administrator control of the server, the company says. Progress published all 31 on October 12 and scored five of them critical. Fixes have been available since September 10, in MarkLogic 11.3.7 and MarkLogic 12.1.0. Affected

The Hacker News
GitLab Patches CVSS 10.0 Flaw That Could Let Unauthenticated Users Run Server Code
The Hacker News3:43 AM

GitLab has released patches for a maximum-severity security flaw impacting its Community Edition (CE) and Enterprise Edition (EE) software that could result in arbitrary code execution. "GitLab has remediated an issue that, under certain conditions, could have allowed an unauthenticated user to execute arbitrary code on the GitLab server via a specially crafted regular expression in a CI/CD

The Hacker News
Low-Cost Android Phones Ship With Preinstalled Malware That Turns Them Into Residential Proxies
The Hacker News1:00 AM

Low-cost Android smartphones have been shipped with malicious software baked into the device firmware, allowing bad actors to covertly install apps, conduct ad fraud, and turn devices into residential proxies. The activity, which targets Android devices built on MediaTek platforms across several brands, is being tracked by Bitdefender under the moniker Midnight Mimosa. The preinstalled

Monday, October 12

BleepingComputer
Anthropic takes risky AI tests offline after models breach govt sites
BleepingComputer1:51 PM

Anthropic announced that its internal AI models undergoing "high-risk and cybersecurity evaluations" no longer have internet access following incidents involving U.S. government websites at the federal, state, and local levels. [...]

The Hacker News
⚡ Weekly Recap: Helpdesk 0-Days, Rogue Certs, ShinyHunters Arrest, AI-Fooling Malware and More
The Hacker News10:16 AM

Some meetings last longer than it took attackers to jump on a newly disclosed security flaw this week. Within hours, they were already testing it. That's not much time to read the warning, let alone do something about it. But speed is only part of the problem. A secure connection didn't always mean a safe destination. People offering to fix a ransomware mess had questions to answer themselves.

Cyber Security News
Ahold Delhaize Takes Systems Offline Following Cybersecurity Incident
Cyber Security News10:12 AM

Ahold Delhaize has taken some systems offline after identifying a security issue within its network, the food retail group said on October 12, 2026. The company, based in Zaandam, the Netherlands, said its teams were assessing the issue and taking steps to limit its impact. Physical stores remain open and continue serving customers. In its […] The post Ahold Delhaize Takes Systems Offline…

Schneier on Security
FBI Arrests Suspect in FBI-Hacking Case
Schneier on Security10:01 AM

In September, hackers from a group called ShinyHunters announced that they stole a trove of FBI data about its own agents. It was an intelligence disaster . Last week, the FBI arrested (alternate link ) someone associated with that crime.

Cyber Security News
Google DevSite Flaw Let Attackers Execute Remote Code Through Forged Flask Sessions
Cyber Security News9:31 AM

A critical vulnerability in Google’s shared DevSite platform could have allowed an unauthenticated attacker to forge Flask session cookies and trigger remote code execution across several Google-owned developer websites, according to researcher Simon Koeck. The issue affected the OAuth flow used by Google developer documentation sites, including developers.google.com, firebase.google.com…

Cyber Security News
Critical GitLab Vulnerability Enables Arbitrary Code Execution Attacks on Servers
Cyber Security News9:19 AM

GitLab has released urgent security updates to fix a critical vulnerability that could allow attackers to execute arbitrary code on affected servers without logging in. Tracked as CVE-2026-97229, the flaw carries the maximum CVSS score of 10.0 and affects both GitLab Community Edition and Enterprise Edition. The company released patches on October 12, 2026. The […] The post Critical GitLab…

Cyber Security News
WhatsApp Attachment Deploys Malware That Gains SYSTEM Access on Windows
Cyber Security News9:02 AM

A malicious WhatsApp attachment is being used to deploy a Windows remote access trojan that can reach SYSTEM-level access, giving its operators deep control over infected machines. The campaign begins with a ZIP archive carrying a financial-document lure and an executable named Statement.exe. Once the recipient opens the file, the malware starts a long, hidden […] The post WhatsApp Attachment…

BleepingComputer
Inside AvisLoader: A Windows Malware Loader Built to Resist Disruption
BleepingComputer9:00 AM

A new Windows malware loader called AvisLoader uses encrypted peer-to-peer communications to make command-and-control infrastructure harder to disrupt. Varonis researchers explain how the malware uses ClickFix delivery, shortcut-based persistence, and remote command execution capabilities. [...]

Cyber Security News
Google AitM Phishing Kit Uses WebSockets to Bypass MFA in Real Time
Cyber Security News8:11 AM

A Google account phishing kit uses live WebSocket connections to guide victims through fake sign-in screens, relay authentication requests, and steal authenticated sessions. The campaign shows how attackers can get past MFA by forwarding login steps in real time rather than breaking the security checks themselves. The operation targets people linked to research organizations in […] The post…

Cyber Security News
Ledger Confirms Unauthorized Hardware Implant in Crypto Wallet Sold by CryptoBilis
Cyber Security News8:10 AM

Ledger has confirmed that a cryptocurrency hardware wallet linked to reported fund losses contained an unauthorized hardware implant, bringing physical tampering into its investigation of devices sold through Southeast Asian reseller CryptoBilis. The finding raises supply chain security concerns, but Ledger has not confirmed how the implant worked or whether it caused every reported theft. […]…

BleepingComputer
GitLab warns of max severity code execution vulnerability
BleepingComputer8:09 AM

GitLab warned users today to immediately patch a maximum-severity vulnerability in the CI/CD Regular Expression Compiler that could let remote attackers run arbitrary code on targeted instances. [...]

Cyber Security News
Attackers Reportedly Hack Supermarket Fridges and Raise Temperatures to 50°C
Cyber Security News7:54 AM

French supermarket chains are dealing with a major cybersecurity incident after attackers reportedly changed refrigeration settings remotely, causing some chilled cabinets and freezers to heat up instead of cool down. The incident began overnight between October 11 and October 12 and affected stores linked to Intermarché, E.Leclerc, and Système U, according to early reports. The […] The post…

Cyber Security News
IBM Patches 22 Verify Access Flaws, Including Critical Remote Code Execution Bugs
Cyber Security News7:07 AM

IBM patched 22 vulnerabilities in Verify Identity Access and Security Verify Access, including two critical flaws allowing unauthenticated remote code execution across appliance and container deployments. The most severe bugs, CVE-2026-78401 and CVE-2026-78406, each carry a CVSS score of 9.8. Both involve deserializing untrusted data, a process where software rebuilds stored or transmitted data…

Cyber Security News
Hackers Exploit Critical AhsayCBS Flaws to Deploy Webshells and XMRig Miners
Cyber Security News6:56 AM

Hackers are exploiting two flaws in AhsayCBS backup servers to run commands, plant webshells, and install XMRig cryptocurrency miners disguised as Microsoft Edge. Huntress first observed exploitation on October 7, 2026, at 23:20:15 UTC. By October 8, its researchers had seen five organizations targeted, with attackers checking systems and setting up tools to maintain access. […] The post Hackers…

The Hacker News
Bring Your Own Agent: Your Employees' Assistants Are Already Logged In
The Hacker News6:55 AM

The personal AI agents rollout is going about as smoothly as expected: Amazon now blocks Meta's Muse because it doesn't identify itself as a bot while browsing; Instinct keeps raising privacy concerns; and the horror stories from pretty much every personal AI agent keep piling up. Regardless, the tech world is mesmerized by the capabilities and potential of these services. Less than a year

Cyber Security News
FBI Arrests Cybersecurity Executive in ShinyHunters-Linked Extortion Investigation
Cyber Security News6:50 AM

The FBI arrested Canadian cybersecurity executive Edward Dubrovsky in Pennsylvania on October 8, 2026, as part of its investigation into the hacking group ShinyHunters. The arrest links a professional involved in ransomware response to an alleged cyber extortion conspiracy. However, the evidence behind the charges remains largely sealed, and the allegations have not been proven […] The post FBI…

The Hacker News
Ledger Finds Unauthorized Hardware Implant in CryptoBilis-Sold Wallet Amid Fund Theft Reports
The Hacker News6:21 AM

Cryptocurrency hardware maker Ledger has temporarily paused sales of its products via CryptoBilis following reports of stolen funds linked to devices sold by the reseller. On Friday, the company said it was investigating reports of loss of funds from users in Southeast Asia who had purchased products from CryptoBilis. The incident is said to have resulted in losses totaling more than $86

Malwarebytes
Phishing emails are baiting your AI assistant
Malwarebytes5:54 AM

If you use an AI assistant to summarize your inbox, hidden instructions could turn a phishing email you wisely ignored into your next to-do item.

The Hacker News
Critical SonicWall SMA 1000 Flaw Targeted in 135 Exploitation Attempts After Patch
The Hacker News5:36 AM

Threat actors have been observed exploiting a recently disclosed critical security flaw in SonicWall Secure Mobile Access (SMA) 1000 appliances within days of public disclosure. The vulnerability, tracked as CVE-2026-102255 (CVSS score: 10.0), is a case of pre-authenticated server-side request forgery (SSRF) that could allow a remote attacker "to direct the appliance to issue requests on their

r/netsec
Hands Off the Keyboard: How AI Agents Run Real Intrusions
r/netsec4:57 AM

New blog: Hands Off the Keyboard Autonomous AI agents running intrusions from recon to root. The operator wrote a goal and read the results. This blog covers real AI attacks happening in the wild. - 75 agent transcripts recovered from the attackers' own servers - Claude Code harness on DeepSeek, plus pi and Codex workers on other models - command execution on 23 hosts, most as root or SYSTEM - a…

The Hacker News
Attackers Exploit CVSS 10.0 Bricksforge WordPress Flaw Enabling Unauthenticated RCE
The Hacker News4:02 AM

A maximum-severity security flaw impacting the Bricksforge plugin for WordPress has come under active exploitation in the wild, according to Patchstack. The critical vulnerability in question is CVE-2026-85097 (CVSS score: 10.0), which allows unauthenticated attackers to upload and execute arbitrary PHP code on vulnerable WordPress websites, resulting in remote code execution (RCE). The

r/netsec
LG webOS sync-demo Preauth RCE
r/netsec3:58 AM

An exploit chain was found in LG webOS, leading to root command execution. The chain starts with a client-key issuance bypass, progresses through service-level access, and ultimately leads to root command execution.

The Hacker News
CyberXero Uses Claude Code in Campaign That Stole Over 628,000 Ukrainian Records
The Hacker News2:26 AM

Cybersecurity researchers have disclosed details of a two-pronged artificial intelligence (AI)-augmented initial access campaign targeting WordPress sites, e-commerce platforms, and critical infrastructure entities in Ukraine. The activity, which brings together commodity offensive tools like Cobalt Strike with an AI orchestration layer powered by Anthropic's Claude Code, has been attributed

Sunday, October 11